Compliance certifications are easy to list on a footer and hard to actually operationalize across a distributed contributor network.
What the certifications cover
SOC 2 and ISO 27001 attest to how data is handled internally — access controls, audit trails, incident response. GDPR and CCPA govern how contributor and end-user data is collected, stored and deleted on request.
Consent at the point of collection
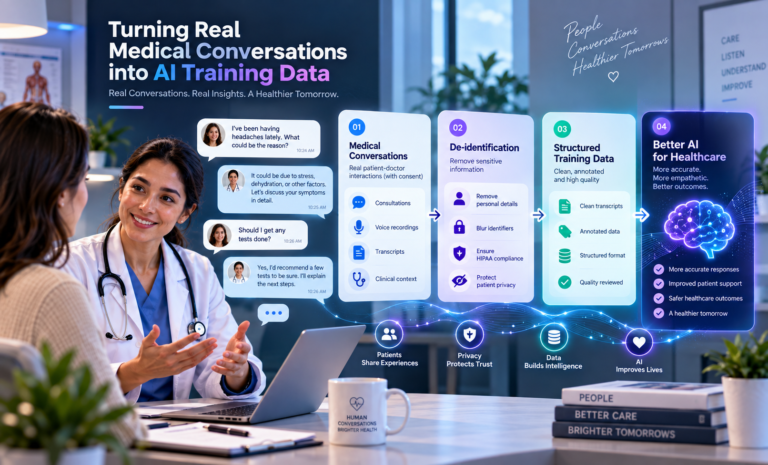
Every contributor explicitly consents to how their data will be used before a single clip is recorded — not retroactively, and not buried in a long terms-of-service document.
Data residency
Some engagements require data to never leave a specific region. That constraint needs to be part of the initial spec, since it affects which contributor pools and storage infrastructure can be used.
Why this matters for procurement
A well-documented compliance posture is often the difference between a data partner clearing legal review in a week versus a quarter.